
Aftonbladet
Abiy Ahmed omvald i Etiopien – attacker i Tigray
Etiopiska angrepp i Tigrayprovinsen har dödat flera personer i ett flyktingläger.
En blandad vy med nyheter från alla kategorier. Perfekt för en snabb daglig överblick utan att växla mellan flöden.
Etiopiska angrepp i Tigrayprovinsen har dödat flera personer i ett flyktingläger.
Etiopiska angrepp i Tigrayprovinsen har dödat flera personer i ett flyktingläger.

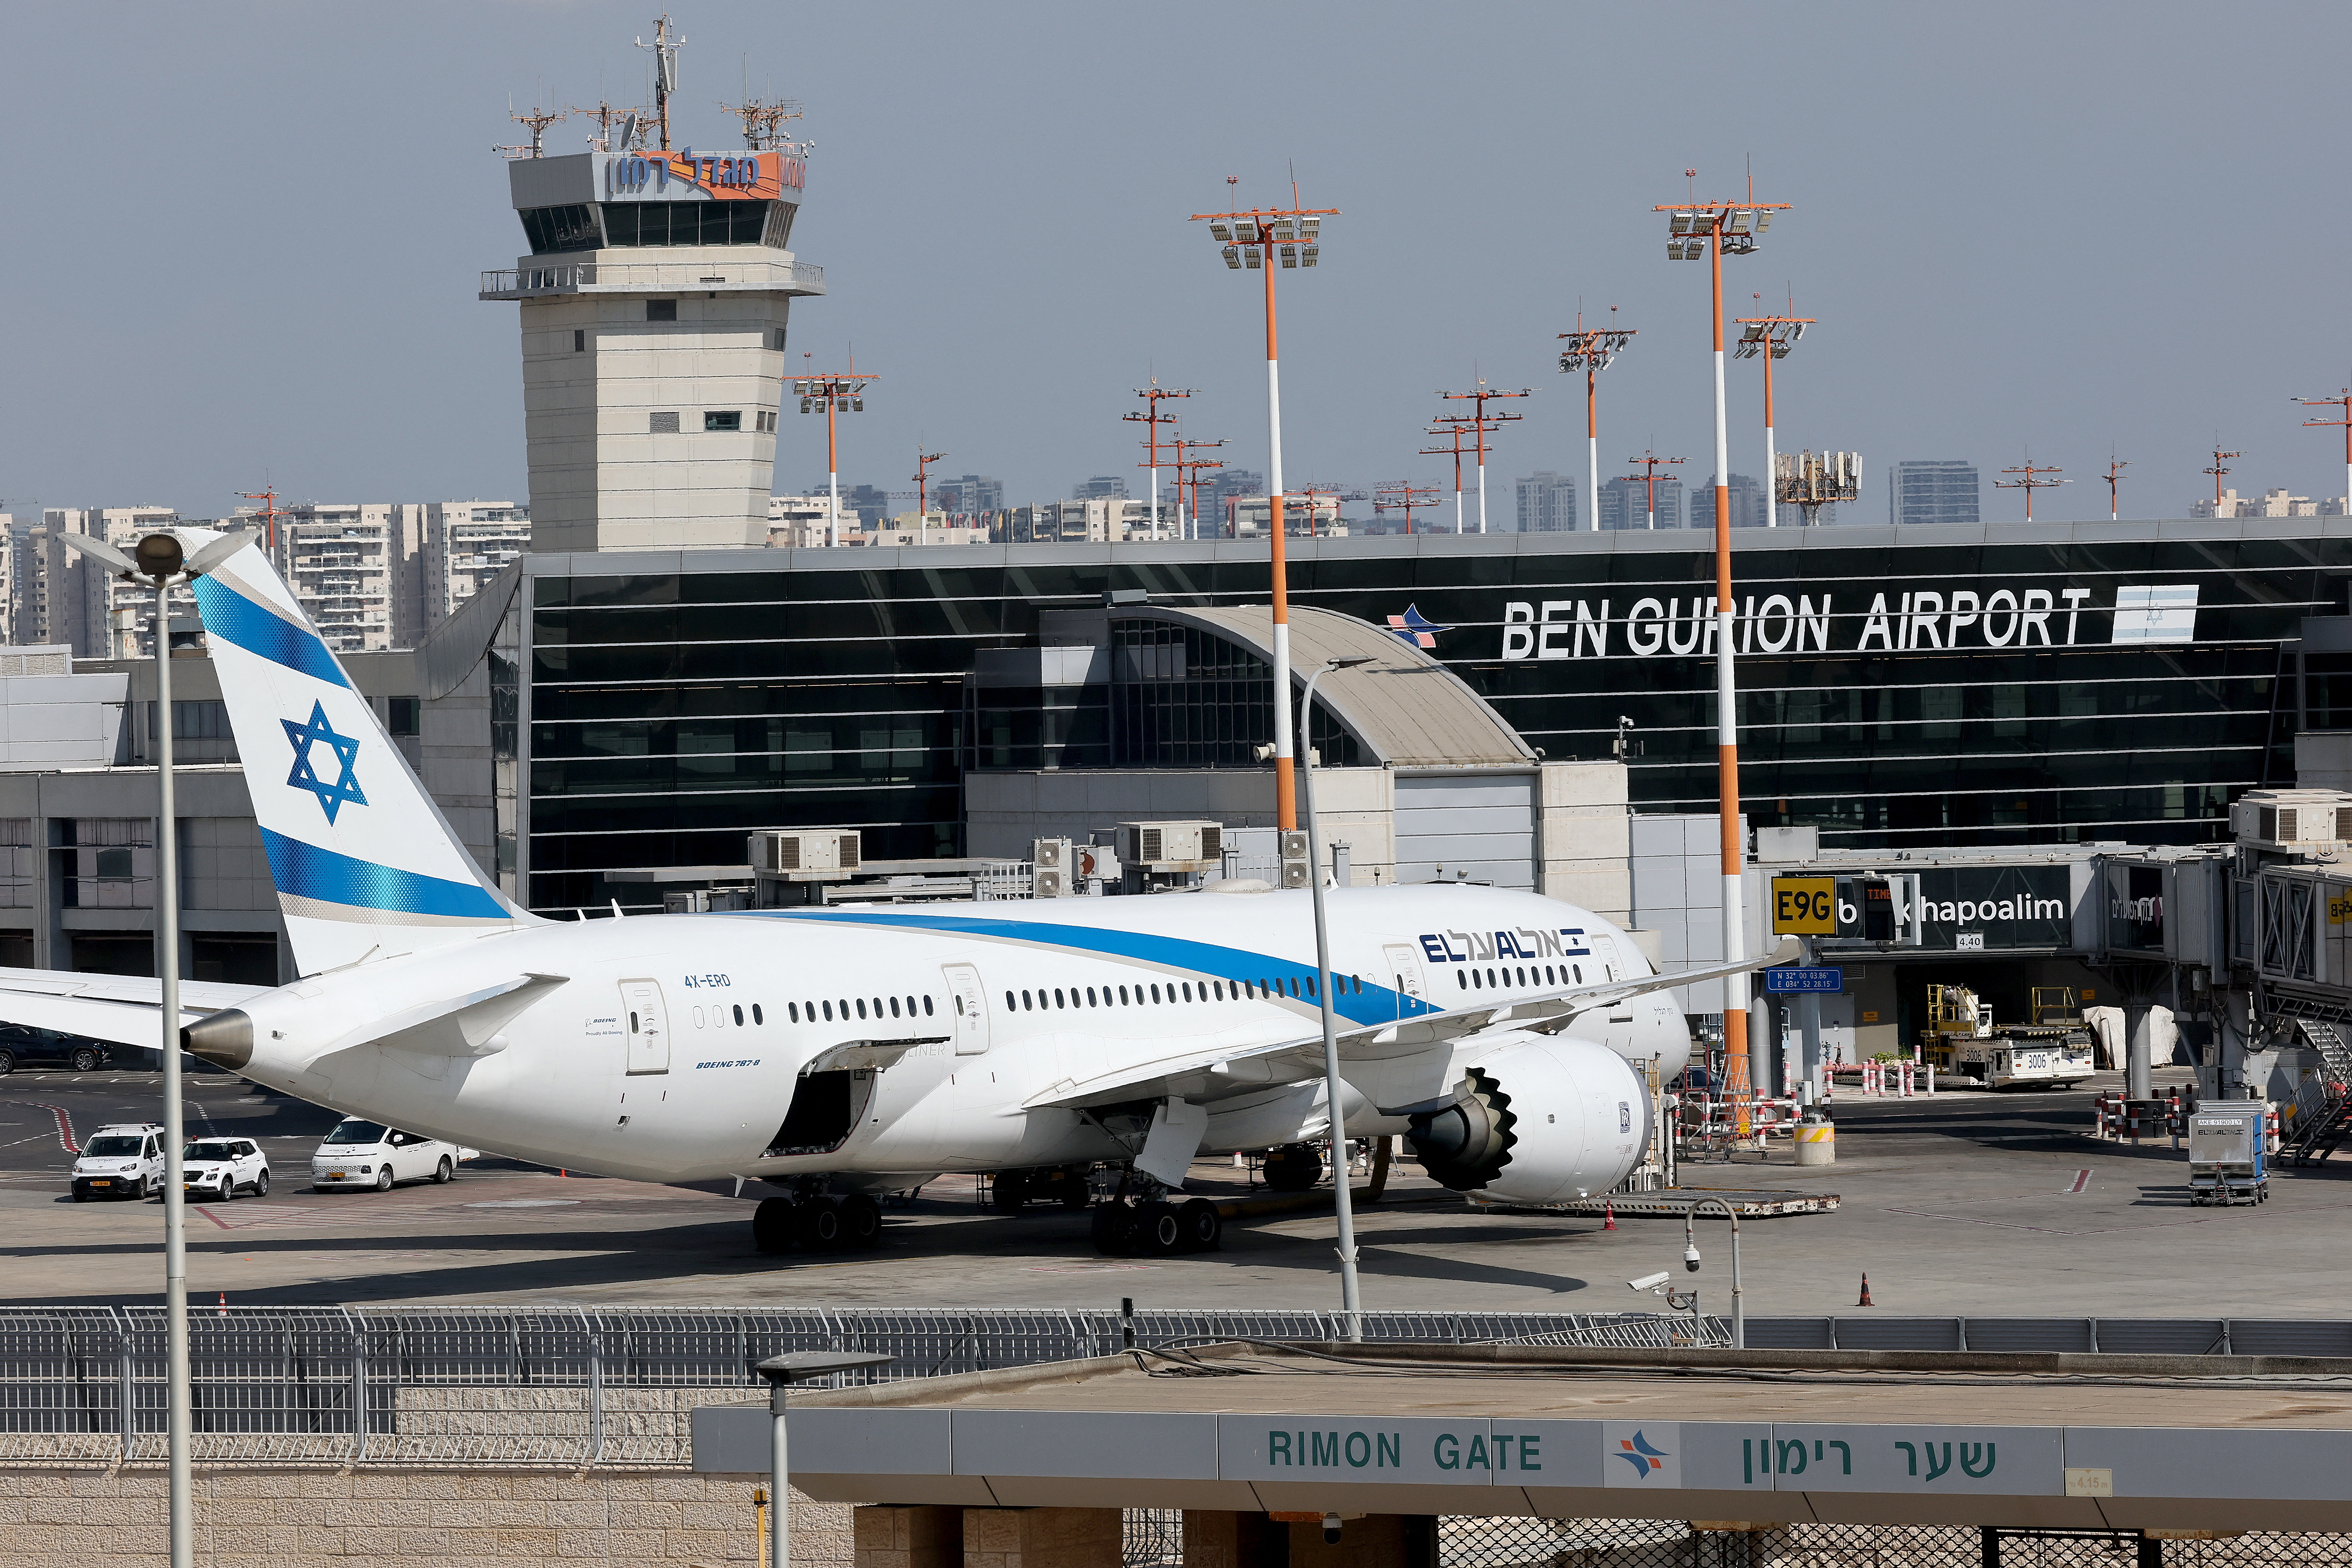
The ongoing investigation has found the attacker intended to crash the plane into Israel's Ben Gurion International Airport, a person familiar with the matter but not authorized to speak publicly told NPR.
Microsoft konstaterar i sin Digital Defense Report 2026 att just nu är det angripare som får ut mest nytta av artificiell intelligens medan försvarare ligger efter. Det hela uppmärksammades först av Bleeping Computer....

## Summary `ZodSmartCoercionPlugin` and `experimental_ZodSmartCoercionPlugin` mishandle object keys that name `Object.prototype` members. Both coerce request input before validation, so any client that can reach a...
Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain conditions. The vulnerability, tracked...
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS score: 9.3), a case of...
A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote attacker to access an affected system with privileges of the admin user. This...
### Summary act_runner appends workflow-controlled `jobs..container.options` directly to the Docker HostConfig for the job container. When runner privileged mode is disabled, only `Privileged` is forced false. Host...
## Overview `probe-image-size` scans the SVG header with a searching regular expression, `/ ]*>/`. On input that contains many ` `, the engine restarts the `[^>]*` scan at every `<` position and runs to end of input...
# Security Advisory — SiYuan Agent Tools SSRF via DNS-Rebinding TOCTOU (Bypass of `CheckHostSSRF`) | Field | Value | |---|---| | **Disclosed by** | joysinleung (`[email protected]`) | | **Report date** |...
# Security Advisory — SiYuan MCP `asset.upload` Reads Arbitrary Absolute File Paths (Workspace Boundary Bypass) | Field | Value | |---|---| | **Disclosed by** | joysinleung (`[email protected]`) | | **Report...
## Summary Using `Database#create_aggregate`, `#create_aggregate_handler`, or `Database#define_aggregator` to define an aggregate function that takes two or more arguments, and then evaluating it over TEXT or BLOB...
Weak authorization in Microsoft Exchange Server allows an authenticated attacker to elevate privileges over a network.
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker tointercept and read sensitive information, including credentials andsession data. The following versions of Johnson Controls...
View CSAF Summary Successful exploitation of these vulnerabilities could enable attackers to gain unauthorized administrative control over vulnerable charging stations or disrupt charging services through denial-of-...
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to gain unauthorized access to the database, execute arbitrary code on the host with the highest level of privilege, or gain...
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to escalate privileges or overwrite files. The following versions of ABB Protection and Control IED Manager PCM600 are...
View CSAF Summary The following versions of CISA Malcolm are affected: Malcolm CVSS Vendor Equipment Vulnerabilities v3 8.8 CISA CISA Malcolm Improper Neutralization of Input During Web Page Generation ('Cross-site...
CVSSv3 Score: 9.8 An Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal') [CWE-22] and Improper Neutralization of NULL Byte or NULL Character [CWE-158] vulnerability may allow an...
Fortinet FortiMail contains a path traversal and an improper neutralization of NULL byte or NULL character vulnerability that may allow an unauthenticated attacker to write arbitrary files on the underlying system via...
Cisco Catalyst SD-WAN Manager contains a hex encoding vulnerability that could allow an unauthenticated, remote attacker to access an affected system with privileges of the admin user due to improper handling of URI...
Citrix NetScaler ADC and NetScaler Gateway contain an improper input validation vulnerability that could allow an unauthenticated attacker to execute arbitrary commands. | Åtgärd: Apply mitigations in accordance with...
Microsoft SharePoint contains a code injection vulnerability which could allow an authorized attacker to execute code over a network. | Åtgärd: Apply mitigations in accordance with vendor instructions, ensuring...
Multiple vulnerabilities in Cisco Identity Services Engine (ISE) and Cisco ISE Passive Identity Connector (ISE-PIC) could allow a remote attacker to access or manipulate data, obtain sensitive information, or cause a...
Update for September 16, 2026: The original 1.0 version of this advisory was specific to the Cisco Adaptive Security Virtual Appliance (ASAv) and Cisco Secure Firewall Threat Defense Virtual (FTDv) models. However, it...