
Dagens Industri
Tankfartyg attackerat i Hormuzsundet
Tolv besättningsmän har skadats i en attack mot en Panamaflaggad oljetanker i Hormuzsundet utanför Oman, enligt Indiens regering.
En blandad vy med nyheter från alla kategorier. Perfekt för en snabb daglig överblick utan att växla mellan flöden.
Tolv besättningsmän har skadats i en attack mot en Panamaflaggad oljetanker i Hormuzsundet utanför Oman, enligt Indiens regering.
Tolv besättningsmän har skadats i en attack mot en Panamaflaggad oljetanker i Hormuzsundet utanför Oman, enligt Indiens regering.
Två fartyg i Svarta havet attackerades av drönare på tisdagen. Ett av fartygen har sjunkit och besättningen saknas. En räddningsoperation pågår. ”Detta är en helt oacceptabel attack och ett grovt brott mot...
Två fartyg i Svarta havet attackerades av drönare på tisdagen. Ett av fartygen har sjunkit och besättningen saknas. En räddningsoperation pågår. ”Detta är en helt oacceptabel attack och ett grovt brott mot...

The ongoing investigation has found the attacker intended to crash the plane into Israel's Ben Gurion International Airport, a person familiar with the matter but not authorized to speak publicly told NPR.
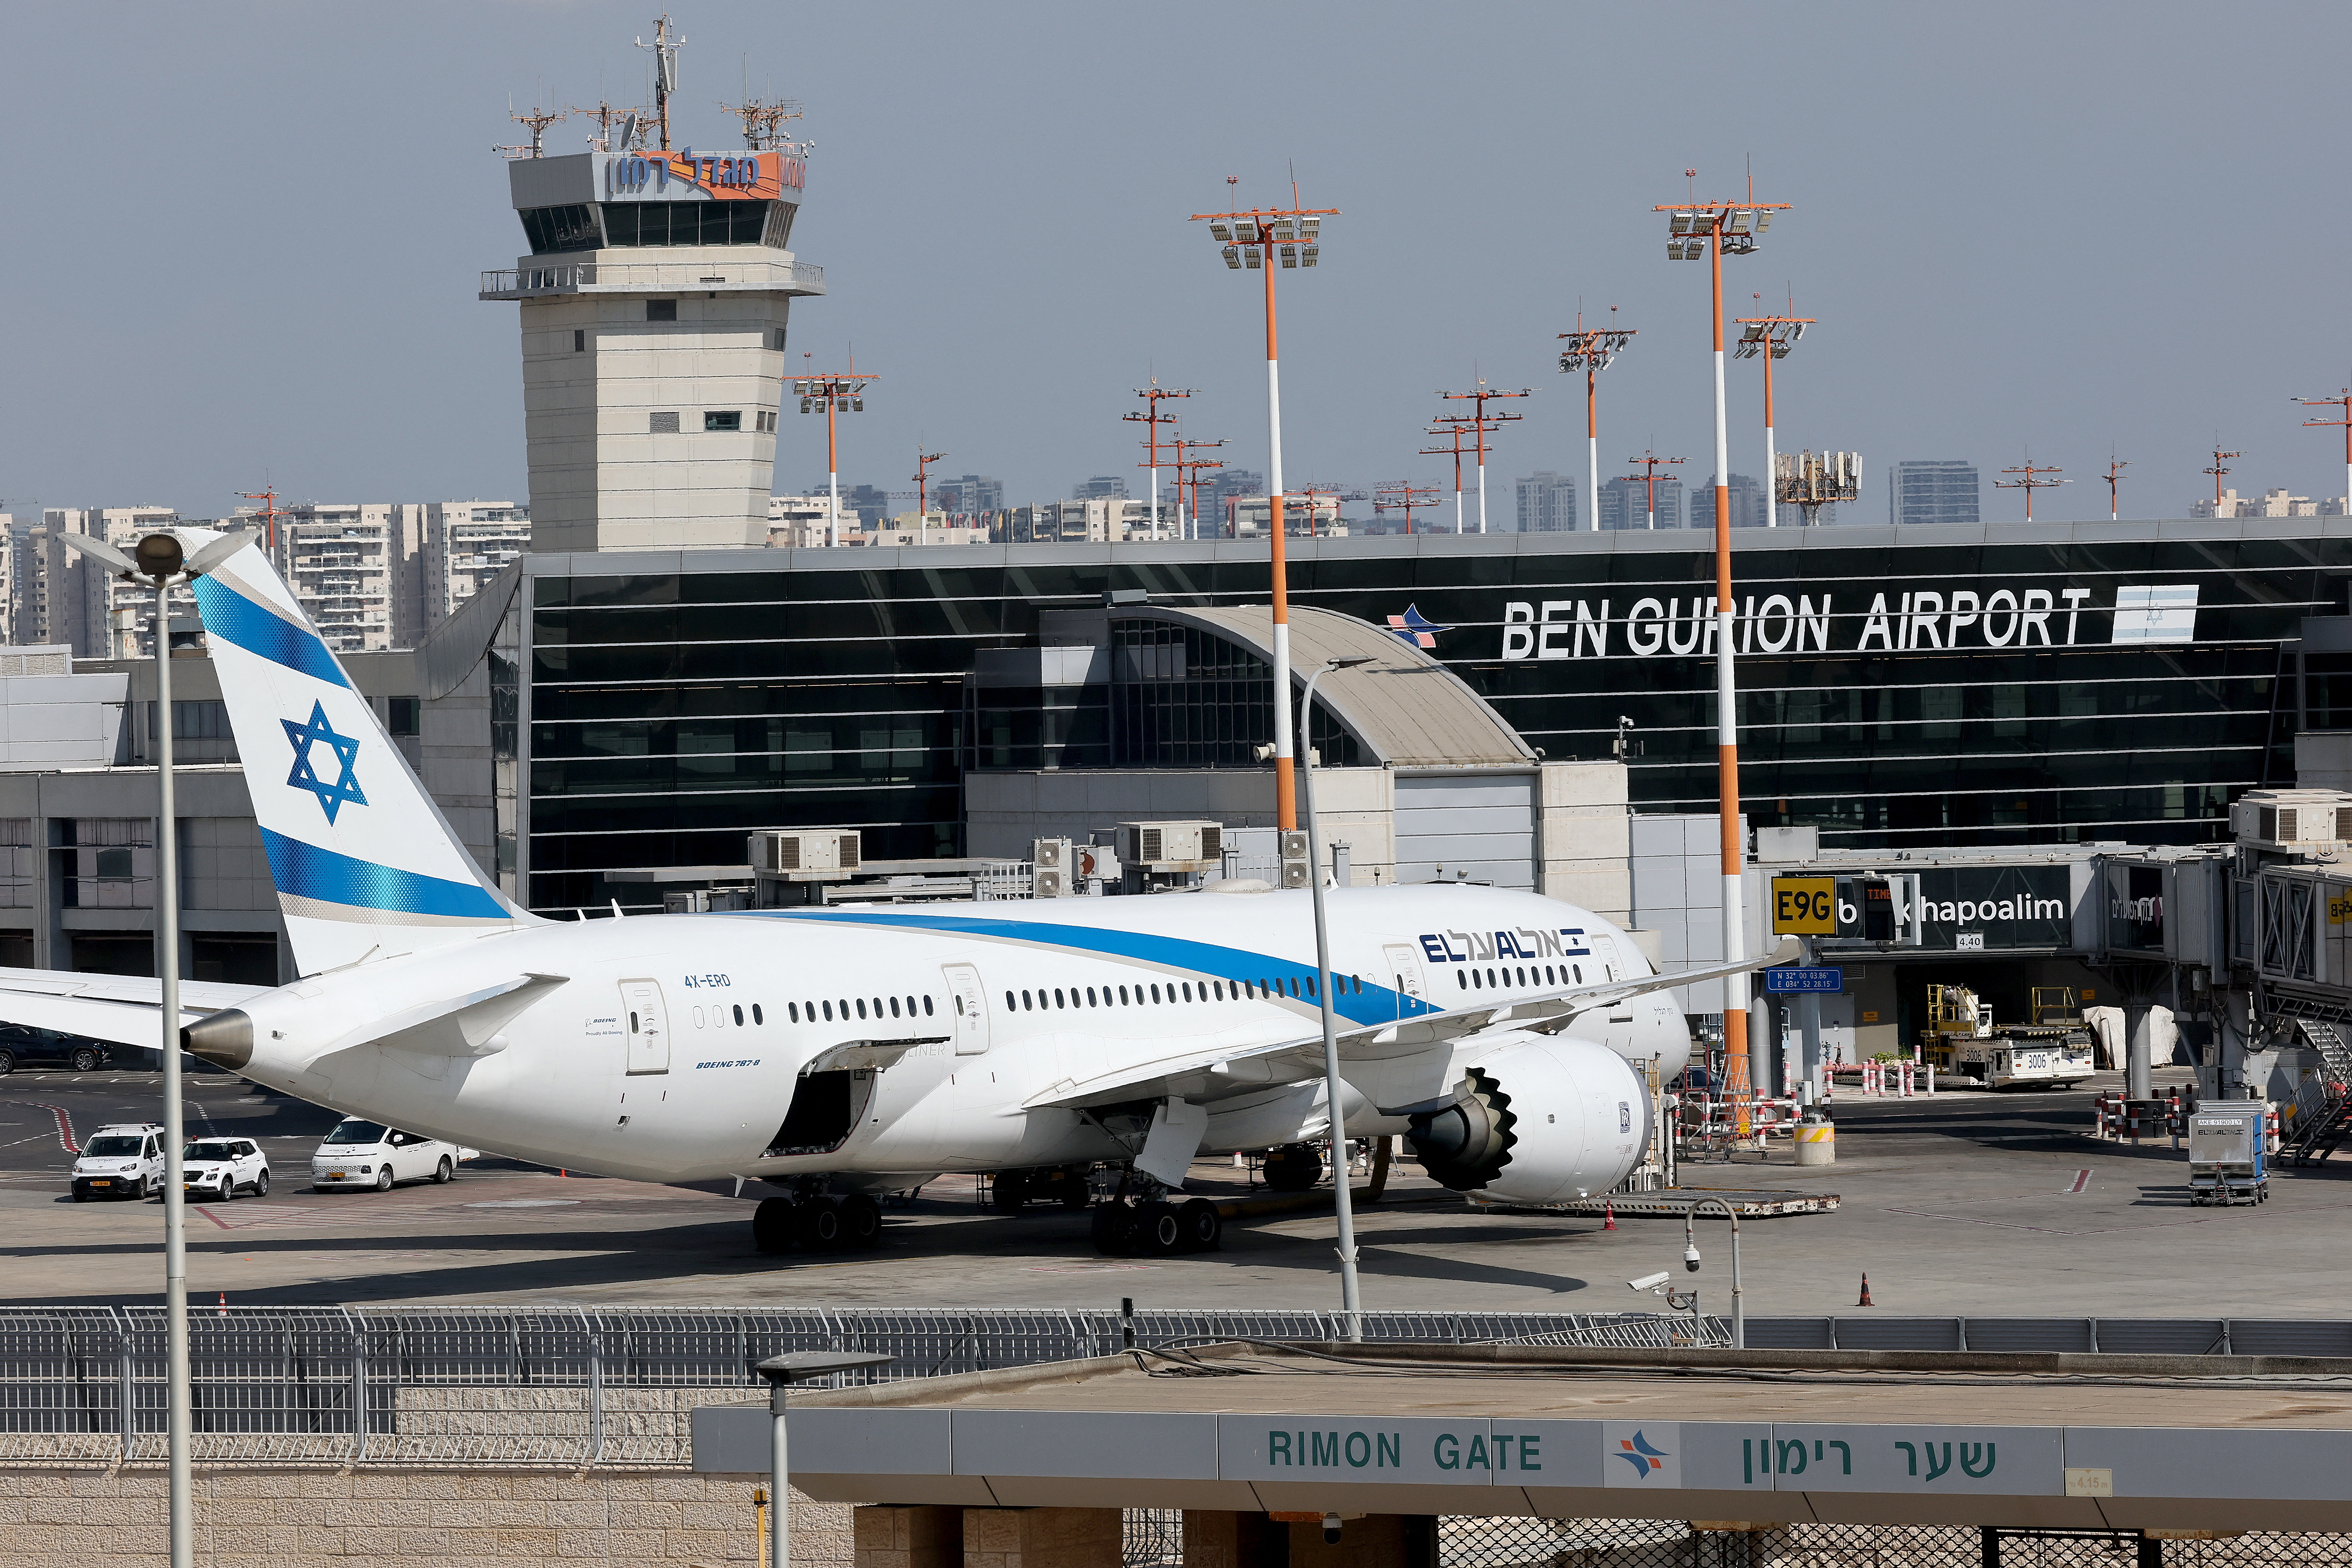

Ny Teknik har talat med två svenska experter om varningssignalerna, de osäkra katastrofprognoserna och vad som måste ske härnäst.

A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in each product's web application root directory. The attacker must...
Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark's national population register, the country's...
### Summary When the HTML backend renders pages in a headless browser (`HTMLBackendOptions(render_page=True)`), the `enable_local_fetch` option is not enforced. A crafted HTML file can embed an arbitrary local file...
## Affected - **Ecosystem / package:** pip / `vllm` - **Affected versions:** vLLM ≤ 0.25.1 (confirmed on 0.25.1, commit [`752a3a504485`](https://github.com/vllm-...
# Security control bypass in `@simple-git/argv-parser`: Git's `VISUAL` editor fallback is not classified as `allowUnsafeEditor` ## Report metadata | Field | Value | | --- | --- | | Package | `@simple-git/argv-parser`...
## Affected product The default `blockUnsafeOperationsPlugin` in `simple-git` when an application permits untrusted values to reach `SimpleGitOptions.config` or Git inline configuration arguments such as `-c =`. ##...
## Summary An OS command injection vulnerability in `git.clone()` allows any application that flows attacker-influenced data into `customArgs` to execute arbitrary code. simple-git 3.36.0 (current latest on npm) ships...
simple-git's blockUnsafeOperationsPlugin blocks dangerous git options (--upload-pack/--receive-pack/--exec/...) unless the consumer opts in via unsafe:{allowUnsafePack:true}. Detection (@simple-git/argv-parser...
### Summary PyMongo percent-decoded the entire host section of a connection string before splitting it into individual `host:port` entries. A percent-encoded `,` or `:` in a hostname therefore decoded into a real...
Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain conditions. The vulnerability, tracked...
A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote attacker to access an affected system with privileges of the admin user. This...
Weak authorization in Microsoft Exchange Server allows an authenticated attacker to elevate privileges over a network.
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker tointercept and read sensitive information, including credentials andsession data. The following versions of Johnson Controls...
View CSAF Summary Successful exploitation of these vulnerabilities could enable attackers to gain unauthorized administrative control over vulnerable charging stations or disrupt charging services through denial-of-...
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to gain unauthorized access to the database, execute arbitrary code on the host with the highest level of privilege, or gain...
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to escalate privileges or overwrite files. The following versions of ABB Protection and Control IED Manager PCM600 are...
View CSAF Summary The following versions of CISA Malcolm are affected: Malcolm CVSS Vendor Equipment Vulnerabilities v3 8.8 CISA CISA Malcolm Improper Neutralization of Input During Web Page Generation ('Cross-site...
CVSSv3 Score: 9.8 An Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal') [CWE-22] and Improper Neutralization of NULL Byte or NULL Character [CWE-158] vulnerability may allow an...
Fortinet FortiMail contains a path traversal and an improper neutralization of NULL byte or NULL character vulnerability that may allow an unauthenticated attacker to write arbitrary files on the underlying system via...
Cisco Catalyst SD-WAN Manager contains a hex encoding vulnerability that could allow an unauthenticated, remote attacker to access an affected system with privileges of the admin user due to improper handling of URI...
Dell Secure Connect Gateway (SCG) Policy Manager, versions prior to 5.34.00.16, Versions prior to 5.36, contains an Improper Certificate Validation vulnerability. An unauthenticated attacker with adjacent network...
Dell Secure Connect Gateway (SCG) Policy Manager, versions prior to 5.34.00.16, contains an Active Debug Code vulnerability. A high privileged attacker with local access could potentially exploit this vulnerability,...
Quick.Cart is vulnerable to Cross-Site Request Forgery in admin config panel. Malicious attacker can craft special website, which when visited by the admin, will automatically send a POST request that changes admin's...